Karl heads up Information Security at Exclaimer, where he’s focused on keeping data secure and ensuring compliance with standards like ISO 27001 and SOC2. With years of hands-on experience, Karl is dedicated to simplifying security processes and staying ahead of potential threats. He’s passionate about using automation and smart practices to strengthen security without adding unnecessary complexity.
How Exclaimer delivers reliability and security at scale
TL;DR
No email content is stored. Emails pass through Exclaimer in transit to apply the correct email signature, then return to your mail flow. No message content, attachments, or subject lines are stored.
Azure-hosted with regional data residency. All processing runs in Microsoft Azure. Customer data stays within the customer's designated region to support GDPR, CCPA, HIPAA, and other data sovereignty requirements.
Encrypted in transit and at rest. Data between Exclaimer and Microsoft 365 or Google Workspace is protected using RSA-2048-bit asymmetric encryption combined with an AES symmetric session key.
Independently certified. Exclaimer holds ISO/IEC 27001:2022 and ISO/IEC 27018:2019 certifications, a SOC 2 Type II attestation, Cyber Essentials certification, and Microsoft 365 Certification, and is rated 100/100 on SecurityScorecard. BARR Advisory completed the ISO and SOC 2 Type II audits in February 2026.
99.99% uptime, active-active failover. Paired Azure datacenters in each region handle the full workload independently, with automatic failover and continuous tenant data synchronization. Real-time status at status.exclaimer.com.
Exclaimer Trust Center. The full certificate listing, audit reports, and answers to 350+ security and compliance questions are available at trust.exclaimer.com.
Before adding any tool to your email environment, IT teams need to know how it handles data, where it runs, and what happens when something goes wrong. This article covers all three.
Exclaimer applies email signatures automatically during mail flow, without storing message content or acting as a delivery dependency. That's the design choice that shapes the reliability and security story, and it's what IT teams most often dig into during evaluation.
The stakes are the reason evaluations get this detailed. The average data breach now costs organizations $4.99 million globally, a record high, according to the IBM Cost of a Data Breach Report 2026. Every additional tool in the email path is another surface a breach investigation has to account for. The questions below are the ones a careful IT or compliance team asks of any email signature vendor, answered here for Exclaimer.
Trusted by 80,000+ organizations worldwide, the platform is built and operated to meet the demands of enterprise email at scale. The sections below walk through how it's architected, how data flows through it, what independent certifications verify, and how the service behaves during an outage.
For the full credentials listing, audit reports, and answers to over 350 security and compliance questions, visit the Exclaimer Trust Center.
Security/reliability area | Exclaimer claim | Evidence |
|---|---|---|
Email content handling | Email content is processed transiently and not stored — no message bodies, attachments, or subject lines are retained | Trust Center |
Hosting | Microsoft Azure — 14 datacenters in 7 geographically separated active-active pairs | Datacenter regions |
Availability | Active-active high-availability design; 99.99% availability SLA. Measured availability of email processing, last 12 months | Status page |
Certifications | SOC 2 Type II attestation, ISO/IEC 27001:2022, ISO/IEC 27018:2019, Microsoft 365 Certification; 100/100 SecurityScorecard | Security accreditations |
Privacy/data residency | EU/EEA data processed in European datacenters; in normal operation, EEA data doesn't leave the EEA | Data residency |
Service monitoring | Real-time service health and incident updates published publicly | status.exclaimer.com |
Data use | Exclaimer reads an email only to decide which email signature applies and where it goes, and processes customer data only to provide the service | Data Processing Agreement |
To see all of our security accreditations, visit the Exclaimer Trust Center. It includes summaries, certificates, reports, policy documents, and answers to over 350 security and compliance questions.
Does Exclaimer store email content?
No. Exclaimer doesn’t store or retain email content. Emails pass through Exclaimer briefly so the correct signature can be applied. Once stamped, the message returns to the mail flow. No content is stored, archived, or accessible to Exclaimer.
This design’s intentional as it limits risk, reduces exposure, and avoids creating a second system of record.
How email processing works
When an email is sent, Exclaimer:
Checks which signature applies
Adds the signature to the message
Immediately returns the email to the mail flow
At no point does Exclaimer store message content, attachments, or conversation history.
Key takeaway
Emails are handled only for the duration required to apply the email signature and are not stored as retained message content.
What data is retained, and why
To support performance and troubleshooting, Exclaimer logs limited metadata for a short time:
Sender and recipient addresses
Signature ID applied
This metadata is retained for up to seven days, then automatically purged. It doesn't include content, subject lines, or attachments.
"The number one question you should ask any supplier is what data they're collecting. It's also the number one question I get asked. Automating signatures by hooking into Entra ID to pull job titles and phone numbers works well, but it grows your data footprint."
That question is the reason Exclaimer's retention window is deliberately narrow. Starting there is how you tell whether a vendor has thought about minimizing what it holds, or just about what it can collect. The service keeps the least it needs to run and troubleshoot (sender address, recipient address, and the applied signature ID) and holds it for up to seven days rather than indefinitely. The email body, subject lines, and attachments are never part of that footprint.
Is email data used for anything else?
Exclaimer reads an email only to decide which email signature applies and where it goes. Under its Data Processing Agreement, Exclaimer processes personal data only on the customer's documented instructions and only to provide the contracted service (clause 2.4). It doesn't sell or share customer personal information with any third party (clause 2.6).
Microsoft Operations Limited is Exclaimer's sole cloud sub-processor. Other sub-processors cover billing, customer support, and other operational functions, and the full list is in Annex 3 of the DPA. Exclaimer gives customers at least 10 days' written notice before engaging a new sub-processor, so they can object before processing begins (clause 3.8).
Customer data is logically segregated by tenant and is never combined with data from other customers.
Why this matters for IT and compliance teams
The practical test for any signature vendor is what it adds to your compliance scope. Processing emails in memory, with no content retention, means:
Lower risk in the event of a breach
Smaller compliance scope
No additional data repository
Alignment with GDPR and other data minimization requirements
For IT and compliance teams, this approach provides centralized email signature control without creating a new data repository or complicating your existing governance model.
How is Exclaimer built for reliability at scale?
Azure is a platform widely trusted by IT teams for running mission-critical services. Exclaimer is designed to operate fully within the Microsoft Cloud environment, allowing emails to be processed securely and consistently without leaving Azure's network.
Optimized for Microsoft Azure from the ground up
Exclaimer's service is architected specifically for Azure, rather than being retrofitted onto a generic cloud platform. That design enables:
Regional deployment aligned to customer location
Built-in scalability to handle growth in users and email volume
Consistent performance across global environments
Microsoft Azure’s own compliance framework underpins this infrastructure, supporting regulatory requirements across regions and industries. Exclaimer builds on those controls with additional service-level safeguards.
High availability and uninterrupted mail flow
Email flow reliability is a non-negotiable requirement for IT teams. Exclaimer addresses this with an active-active High Availability Cluster (HAC) model.
When the service is operating normally:
Emails are processed by paired Azure datacenters within the same region
Traffic is distributed using automated load balancing
Each datacenter can handle the full regional load if required
If an issue affects one Azure datacenter, Exclaimer automatically switches processing to the alternate datacenter. This happens without manual intervention and without interrupting email delivery.
Load balancing and fault handling
Exclaimer uses Azure-native load balancing to reduce risk and maintain service continuity. Key elements include:
Automated traffic distribution across regional datacenters
Continuous synchronization of tenant data within the region
The ability to remove a datacenter from rotation automatically or manually if needed
This approach minimizes single points of failure and supports Exclaimer's 99.99% service availability. Real-time and historical status available at status.exclaimer.com.
Data handling within regional clusters
All data required to operate an Exclaimer subscription is hosted securely in Microsoft Azure. Data is stored within a High Availability Cluster in the customer's designated region, which means:
Data residency is maintained by design
Customer data isn't stored outside the assigned geography
Requirements under GDPR, CCPA, and similar regulations are supported
This includes configuration data, email signature templates, and directory attributes. Email message content isn't stored as part of this process.
Stored data is encrypted at rest with AES-256. When a subscription ends, Exclaimer deletes all personal data it processed on the customer's behalf, or returns it at the customer's choice, and certifies that it has done so.
Secure connections and service hardening
All connections to and within the Exclaimer service are secured using SSL certificates and TLS encryption. These connections are continuously monitored to meet current cloud security standards.
Before any updates are deployed:
Changes are built and tested by Exclaimer's development and QA teams
Services are stress-tested beyond normal usage levels
Code is scanned for malware and verified using native Azure antimalware tools
Updates are rolled out out of hours for each region to minimize operational impact.
Global availability by design
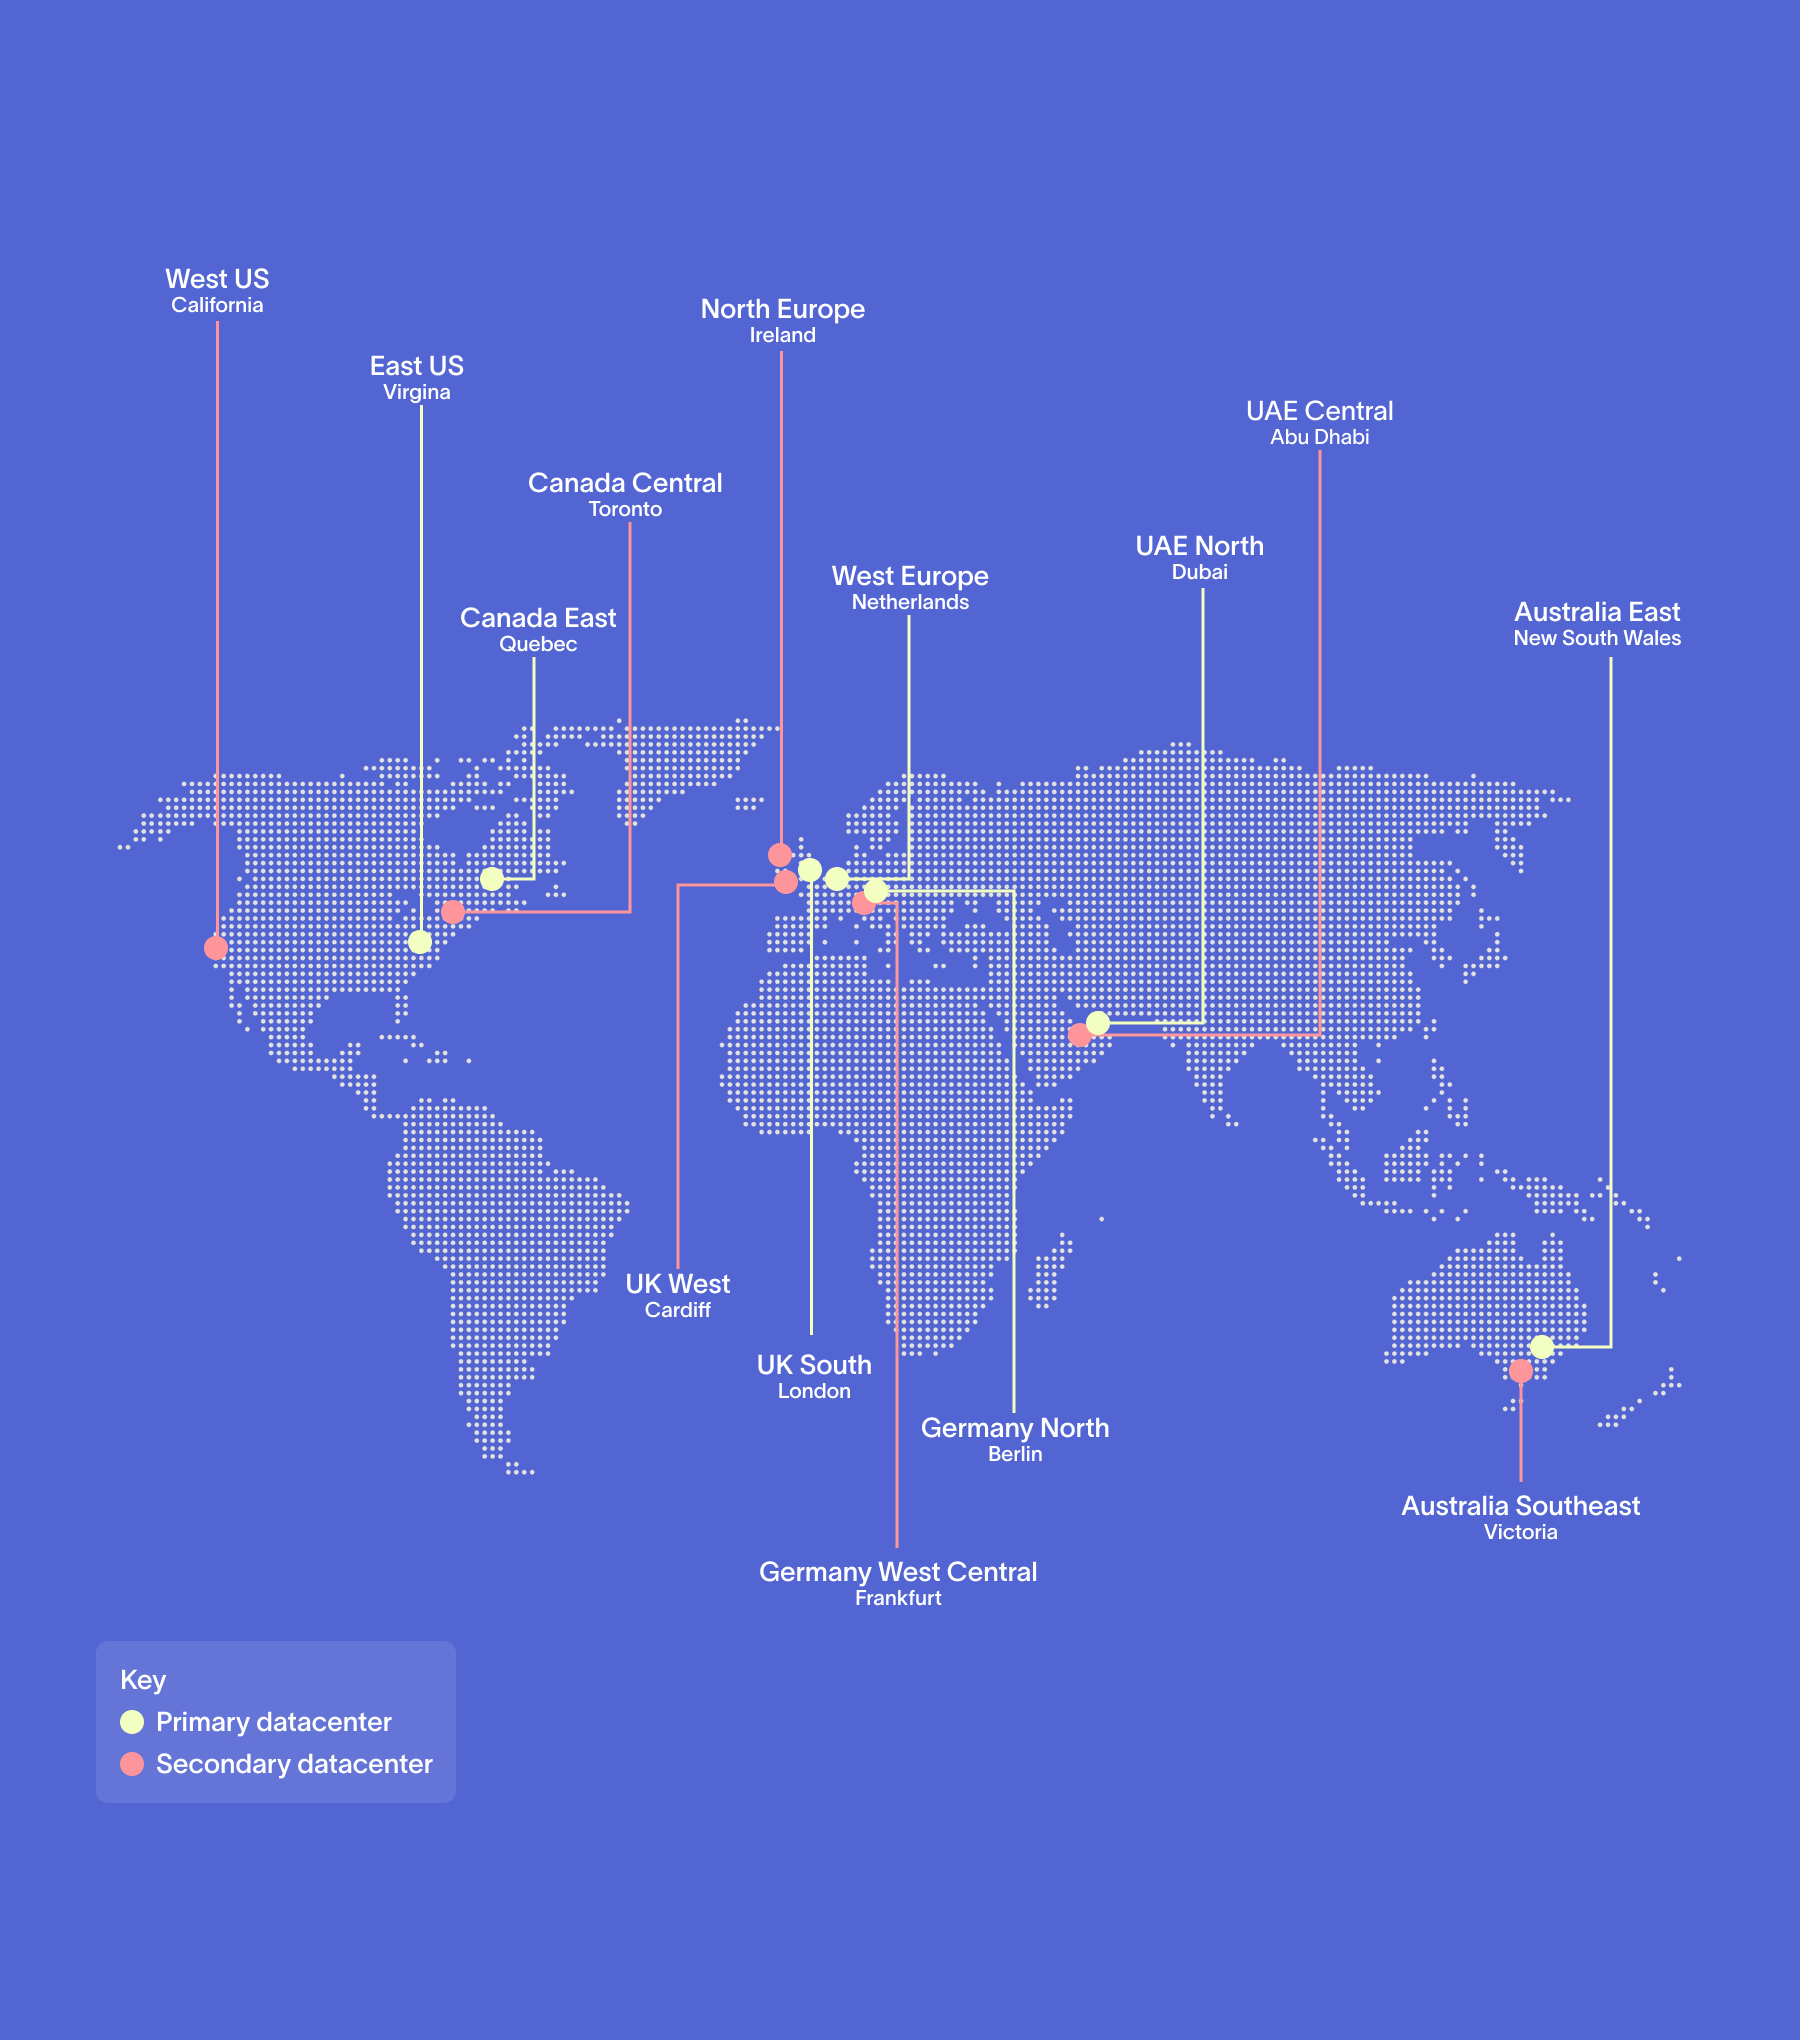
Exclaimer operates across 14 Microsoft Azure datacenters worldwide, arranged in seven geographically separated active-active pairs. This global footprint allows Exclaimer to keep customer data within geographic boundaries, deliver consistent performance across regions, and protect against local Azure infrastructure issues. Each regional datacenter pair is designed so that either location can support the full workload if required.
Region | Primary Datacenter | Secondary Datacenter | Status page prefix |
|---|---|---|---|
USA | East US — Virginia | West US — California | US |
Canada | Canada Central — Toronto | Canada East — Quebec | CA |
Europe | West Europe — Netherlands | North Europe — Ireland | EU |
UK | UK South — London | UK West — Cardiff | UK |
Germany | Germany West Central — Frankfurt | Germany North — Berlin | DE |
Australia | Australia East — NSW | Australia Southeast — Victoria | AU |
Middle East (UAE) | UAE North — Dubai | UAE Central — Abu Dhabi | UAE |
For the full mapping of regions to datacenters, see the cloud endpoints page.
IT teams can check system status anytime via Exclaimer’s Service Health page, which offers real-time performance and incident updates.
What security certifications and compliance standards does Exclaimer meet?
Exclaimer is independently audited and certified against globally recognized security and privacy standards, including SOC 2 Type II, ISO 27001, ISO 27018, and Microsoft 365 Certification.

These certifications validate how Exclaimer is built, operated, and governed. They provide external assurance that security, availability, confidentiality, and privacy controls are not only defined but consistently followed in practice.
Standard | Type | Issuer or auditor | Latest audit or renewal | Cycle or validity | Evidence |
|---|---|---|---|---|---|
ISO/IEC 27001:2022 | Certification | BARR Advisory (ANAB-accredited), certificate 011588-01 | February 2026 | Annual surveillance audits; full recertification every three years | ISO 27001 |
ISO/IEC 27018:2019 | Certification | BARR Advisory (ANAB-accredited), certificate 011588-04 | February 2026 | Annual surveillance audits; full recertification every three years | ISO 27018 |
SOC 2 Type II | Attestation report (Security, Availability, Confidentiality) | BARR Advisory, P.A. | Audit completed February 2026 | Annual audit across a 12-month observation period | SOC 2 |
Microsoft 365 Certification | Microsoft review | Microsoft | February 2026 | Renewed every 12 months | Certification |
Cyber Essentials | UK scheme backed by the NCSC, standard tier | Cyber Aggress (IASME-licensed), certificate ecb1dcca-ef20-4306-beea-39087d1d9e51 | November 22, 2025 | Held since January 2022; recertification due November 22, 2026 | Cyber Essentials |
CSA STAR Level 1 | Self-assessment (CAIQ against Cloud Controls Matrix v4), not externally audited | Published in the CSA STAR Registry | Renewed annually | Listed since July 16, 2020 | CSA STAR |
PCI DSS | Self-assessment questionnaire, not an external audit | Exclaimer (internal) | Reviewed annually | Card payments handled by a PCI DSS-certified third-party provider | PCI DSS |
SecurityScorecard | Continuous third-party rating | SecurityScorecard | A (100/100), last reviewed May 2026 | Rated A since 2021 | Rating |
SOC 2 Type II
Exclaimer holds a SOC 2 Type II attestation, confirming that its systems meet the Trust Services Criteria: security, availability, and confidentiality.
A SOC 2 Type II report evaluates how controls operate over an extended period rather than at a single point in time. This demonstrates that Exclaimer's safeguards are consistently applied during day-to-day service delivery, not just defined on paper. BARR Advisory, an AICPA-registered audit firm, audits Exclaimer every year across a continuous 12-month observation period. The most recent audit was completed in February 2026, and the report is available in the Trust Center under NDA.
Within the email signature management category, Exclaimer is the only dedicated provider that publicly lists both ISO 27001 and SOC 2 Type II. Many vendors hold one or the other; Exclaimer holds both, publicly.
For customers operating under regulated environments — including HIPAA— this attestation provides independent assurance that controls supporting data protection, access management, and service availability are effective.
ISO/IEC 27001
Exclaimer has been certified to ISO/IEC 27001 since 2016. The current certificate is issued by BARR Advisory, an ANAB-accredited certification body. This international standard defines how to establish, operate, monitor, and continually improve an Information Security Management System (ISMS) covering people, processes, and technology. Certification means Exclaimer undergoes regular independent audits to confirm ongoing compliance with internationally accepted security controls.
The renewed certification, announced on February 26, 2026, is to the 2022 version of the standard. Surveillance audits run every year, with a full recertification every three years.
ISO/IEC 27018
Exclaimer is also certified to ISO/IEC 27018, an extension of ISO 27001 focused on privacy protections for personally identifiable information (PII) in cloud services. This standard introduces additional controls for secure PII handling, transparency around data use, and rights related to the use of personal data.
The renewed certification is to the 2019 version, ISO/IEC 27018:2019.
Microsoft 365 Certification
Exclaimer is a Microsoft 365 Certified application, following a detailed security review and audit conducted by Microsoft. This certification verifies that the application integrates securely with Microsoft 365, data handling aligns with Microsoft's security requirements, and the service meets Microsoft's standards for cloud applications.
GDPR and global data privacy regulations
Exclaimer supports GDPR requirements through regional data processing, documented data processing terms, security certifications, and privacy controls. Exclaimer is regularly audited to confirm ongoing adherence. Full compliance documentation, including the DPA, is available at the Exclaimer Trust Center.
Exclaimer is a data processor under GDPR Article 28. Its Data Processing Agreement is incorporated into its End User Licence Agreement (EULA), so customers who accepted the EULA since May 2018 are covered automatically, and standalone DPAs are available on request. Karl Bagci, Director of IT & Information Security, is Exclaimer's Data Protection Officer.
For customers in the EU and EEA, personal data is processed within European datacenters — specifically Germany, the Netherlands, and Ireland. In normal operation, EEA personal data doesn't leave the EEA, and UK customer data is hosted in the United Kingdom. If technical support is provided from outside the EEA, EU Standard Contractual Clauses cover the transfer.
Exclaimer also aligns with other global privacy frameworks, including:
UK GDPR
- California Consumer Privacy Act (CCPA)
HIPAA
DIFC and ADGM data protection regulations
Under the CCPA, Exclaimer acts as a service provider. Under the other comprehensive U.S. state privacy laws, it acts as a processor. U.S. customer data is processed in the East US (Virginia) and West US (California) datacenters.
Cyber Essentials
Exclaimer is certified under the UK government-backed Cyber Essentials scheme, managed by the National Cyber Security Centre (NCSC). Cyber Essentials demonstrates that essential cyber hygiene practices are in place to protect systems from common internet-based threats.
Exclaimer has held the certification continuously since January 2022. Cyber Aggress, an IASME-licensed certification body, issued the current certificate on November 22, 2025. It covers the whole organization and is the standard Cyber Essentials tier, not Cyber Essentials Plus. Recertification is due by November 22, 2026.
Cloud Security Alliance (CSA)
Exclaimer's cloud solution has been listed in the public CSA STAR Registry since July 16, 2020, with a STAR Level 1 self-assessment (the Consensus Assessments Initiative Questionnaire, mapped to Cloud Controls Matrix v4) that Exclaimer renews every year. Level 1 is a self-assessment, not an independent audit.
Exclaimer is a CSA Corporate Member and carries the CSA Trusted Cloud Provider trustmark. Anyone can download the questionnaire from the registry without an account or an NDA.
PCI DSS and payment security
Exclaimer is tested quarterly against PCI DSS requirements to validate secure handling of payment-related processes.
Exclaimer does not store credit or debit card details.
Payment transactions are handled separately via a PCI-compliant payment portal secured with high-grade SSL encryption.
Continuous protection and monitoring
Security and data protection are embedded into Exclaimer’s operations, including:
Regular third-party penetration testing and vulnerability scanning
Internal security training for teams
Independent audits and compliance assessments
A 100/100 rating on SecurityScorecard, reflecting a strong external security posture and low vulnerability risk.
Control | Details | Frequency | Evidence |
Service monitoring | 24/7/365 automated monitoring; real-time alerts and predefined escalation chains | Continuous | status.exclaimer.com |
Penetration testing | Third-party security testing | Regular | Penetration test report |
Vulnerability scanning | Continuous scanning | Continuous | Vulnerability and change management |
Security training | Internal program for all teams | Continuous | Employee security and awareness |
Code scanning | Native Azure antimalware scanning on every build; verified before deployment | Every build | Azure antimalware tooling |
Change deployment | Built, QA-tested, stress-tested beyond peak load; staged regional rollout out of hours | Every release | Release notes |
What happens if Exclaimer experiences an outage?
The short answer is that email continues to flow. Exclaimer's designed so that a service disruption does not stop or block email delivery.
Reliability is critical for any system involved in email infrastructure. Exclaimer avoids single points of failure and handles faults transparently, without requiring action from IT teams or end users.
Continuous monitoring and automated response
Exclaimer’s service is monitored 24/7/365. Automated monitoring detects service alerts in real time and triggers predefined escalation chains. The primary objective is to maintain uninterrupted mail flow for all customers.
If an issue is detected at one regional datacenter, processing automatically shifts to the alternate location. Tenant data is continuously synchronized, so continuity is maintained without manual intervention. Once the issue is resolved, the service continues operating as normal.
No impact on mail delivery
Exclaimer applies email signatures during message processing. However, it doesn't act as a mail transfer agent (MTA) and doesn't replace native Microsoft 365 or Google Workspace mail delivery. This means:
Emails aren't queued or blocked by Exclaimer
Mail continues to be delivered by the underlying email platform
Email signature application resumes automatically when the service is fully available
This prevents Exclaimer from becoming a single point of failure in email delivery.
Failure scenario | Mail delivery impact | Email signature impact | Recovery |
Exclaimer processing unavailable | Delivery continues through Microsoft 365 or Google Workspace — Exclaimer is not the MTA | Email signature may not be applied until service resumes or fails over | Automatic failover to paired regional datacenter |
Azure regional issue | Traffic fails over to paired datacenter automatically; no manual intervention required | Email signature processing continues or resumes after failover | Architecture/SLA |
Planned maintenance | No impact on mail delivery | Defined per maintenance notice | status.exclaimer.com |
Keeping pace with the Azure platform
Exclaimer’s development and QA teams continuously update the service to align with changes in Microsoft Azure. All updates are built, tested, and validated before deployment, including stress testing beyond normal usage to prevent upstream issues.
How does Exclaimer process emails?
Emails are processed in memory, encrypted in transit, and never stored permanently. When an email reaches the Exclaimer service, it's inspected only to determine whether a signature should be applied and where it should be placed.
Message inspection and signature application
During processing, Exclaimer:
Checks the sender, recipient, and subject line
Determines whether an email signature should be added or excluded
Decodes the message format (MIME or TNEF) to identify the correct placement
If an email is sent in Rich Text or Plain Text, it's converted to HTML so a complete HTML email signature can be applied consistently.
Sender information is retrieved from cached directory data (Microsoft Entra ID or Google Workspace Directory) and any approved custom attributes. These details are inserted into the assigned email signature design, and the email is returned to the Microsoft 365 or Google Workspace tenant.
Encryption and data protection
All data in transit between Exclaimer and Microsoft 365 or Google Workspace is encrypted using RSA-2048-bit asymmetric encryption combined with a one-time AES (Rijndael) symmetric session key. AES is the Advanced Encryption Standard selected by the U.S. National Institute of Standards and Technology (NIST) and is widely used to protect sensitive data in transit. Encryption keys are issued and managed through certificates, with separate keys used specifically for encryption and decryption.
No permanent storage of email content
Exclaimer doesn't permanently store emails. Messages are processed in memory and encrypted at rest only for the time required to apply the email signature. For support and troubleshooting purposes, Exclaimer temporarily logs a minimal set of metadata for up to seven days:
Sender address
Recipient address
Applied email signature ID
Message content, subject lines, and attachments aren't stored.
Encrypted messages and bypass behavior
If an email is already encrypted before reaching Exclaimer — such as with S/MIME, Microsoft OME, or IRM — the imprinting service can't modify it. In these cases, the message bypasses email signature processing and is delivered unchanged. Encryption and privacy are fully preserved.
How does Exclaimer handle client confidentiality and PHI?
Exclaimer processes signature metadata — sender name, role, and contact details — and the email envelope required to apply an email signature. It doesn't store the email body or attachments. Protected Health Information (PHI) in the email body is never persisted by Exclaimer.
For organizations in regulated industries, that distinction matters. Healthcare teams operating under HIPAA and financial organizations subject to client confidentiality requirements need a clear account of what Exclaimer touches, what it does not, and how data in transit is protected.
What Exclaimer processes and doesn't store:
Processes: Sender address, recipient address, and the email header required to match and apply a Signature Rule
Processes: Directory attributes used to personalize the email signature — name, job title, phone number, department
Does not store: Email body text
Does not store: Email attachments
Does not store: Subject lines
Temporarily retains (up to seven days, for support purposes only): Sender address, recipient address, and the applied Signature Rule ID. This does not include message content.
Data in transit between Exclaimer and Microsoft 365 or Google Workspace is encrypted using Transport Layer Security (TLS) 1.2 or higher, combined with RSA-2048-bit asymmetric encryption and an AES symmetric session key. Data at rest is encrypted using AES during the brief window required to apply the email signature.
For PHI specifically: the email body — where Protected Health Information (PHI) would typically appear under 45 CFR § 164.312 — is never read beyond what is necessary to determine email signature placement, and is never written to disk. Exclaimer is HIPAA-compliant, and a Business Associate Agreement (BAA) is available upon request through the Exclaimer Trust Center.
Exclaimer's data processing activities are governed by its Data Processing Agreement (DPA).
Why reliability and security matter for IT teams evaluating Exclaimer
For IT teams, email signatures are part of how an organization controls outbound communications at scale.
Exclaimer is built to support that responsibility without adding risk. Reliability keeps mail flowing under all conditions. Governance applies branding, disclaimers, and identity under policy. Security keeps the service operating safely within Microsoft 365 or Google Workspace.
Exclaimer has clear boundaries. It doesn't detect or block threats and doesn't replace your existing governance stack. Instead, it acts as a governed layer for standardizing email signatures — without storing message content or creating a delivery dependency.
For teams assessing vendor risk, this reduces the evaluation scope:
Email remains under your mail platform's control
Email signatures are managed centrally under defined policy
Security practices are independently audited and verifiable
For the full credentials listing, certification reports, and the complete security and compliance FAQ, visit the Exclaimer Trust Center.